How we protect data
The Registry is designed so that each use of the data receives only what it needs, and so that identifiable information is disclosed only for specific, approved purposes.
Pseudonymisation
The Registry does not hold patients' names. Identifiers such as NHS numbers are kept apart from the data used for analysis. When an approved project needs individual records, identifiers are removed and replaced with codes (pseudonyms) made for that project alone. The key linking those codes to patients stays with the Registry and is never given to the project. Dates are released only at the precision a project needs, for example as intervals from referral rather than calendar dates.
How each use is classified
Every use of Registry data falls into one of these tiers:
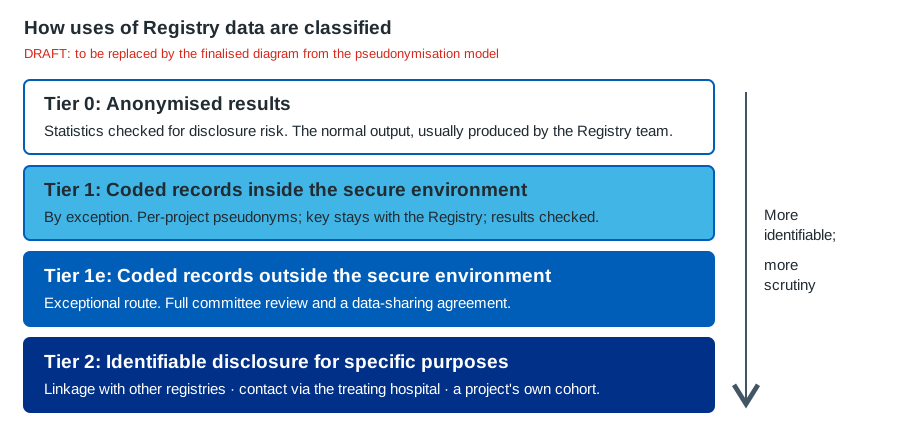
- Tier 0: anonymised results. Statistics and other results that cannot identify anyone, checked for disclosure risk before release. This is the normal output, usually produced by the Registry team.
- Tier 1: coded records inside the secure environment. By exception, an approved project's analyst works with pseudonymised records inside the Registry's trusted research environment. Activity is logged, no copies leave, and results are checked before release.
- Tier 1e: coded records outside the secure environment. An exceptional route, for example where a project must combine Registry data with other registries' data elsewhere. It needs full committee review and a data-sharing agreement that forbids re-identification and onward sharing.
- Tier 2: identifiable disclosure for specific purposes. Linking records with other national registries, asking a patient's treating hospital to contact them about a study, or supplying Registry data about a project's own cohort on that project's own legal basis.
Patients who have opted out or objected are never included in identifiable disclosures (Tier 2) or in releases outside the secure environment (Tier 1e).
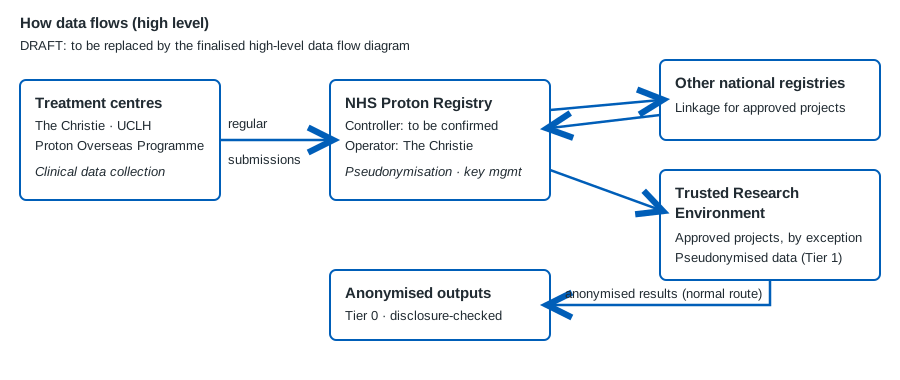
How data flows
Assurance
- Our approach follows the Five Safes framework: safe projects, safe people, safe settings, safe data and safe outputs.
- Everything that leaves the secure environment and is derived from Registry data passes the Registry's output checks.